
HackNotice Launches Agentic Credential Defense to Find and Invalidate Stolen Valid Accounts
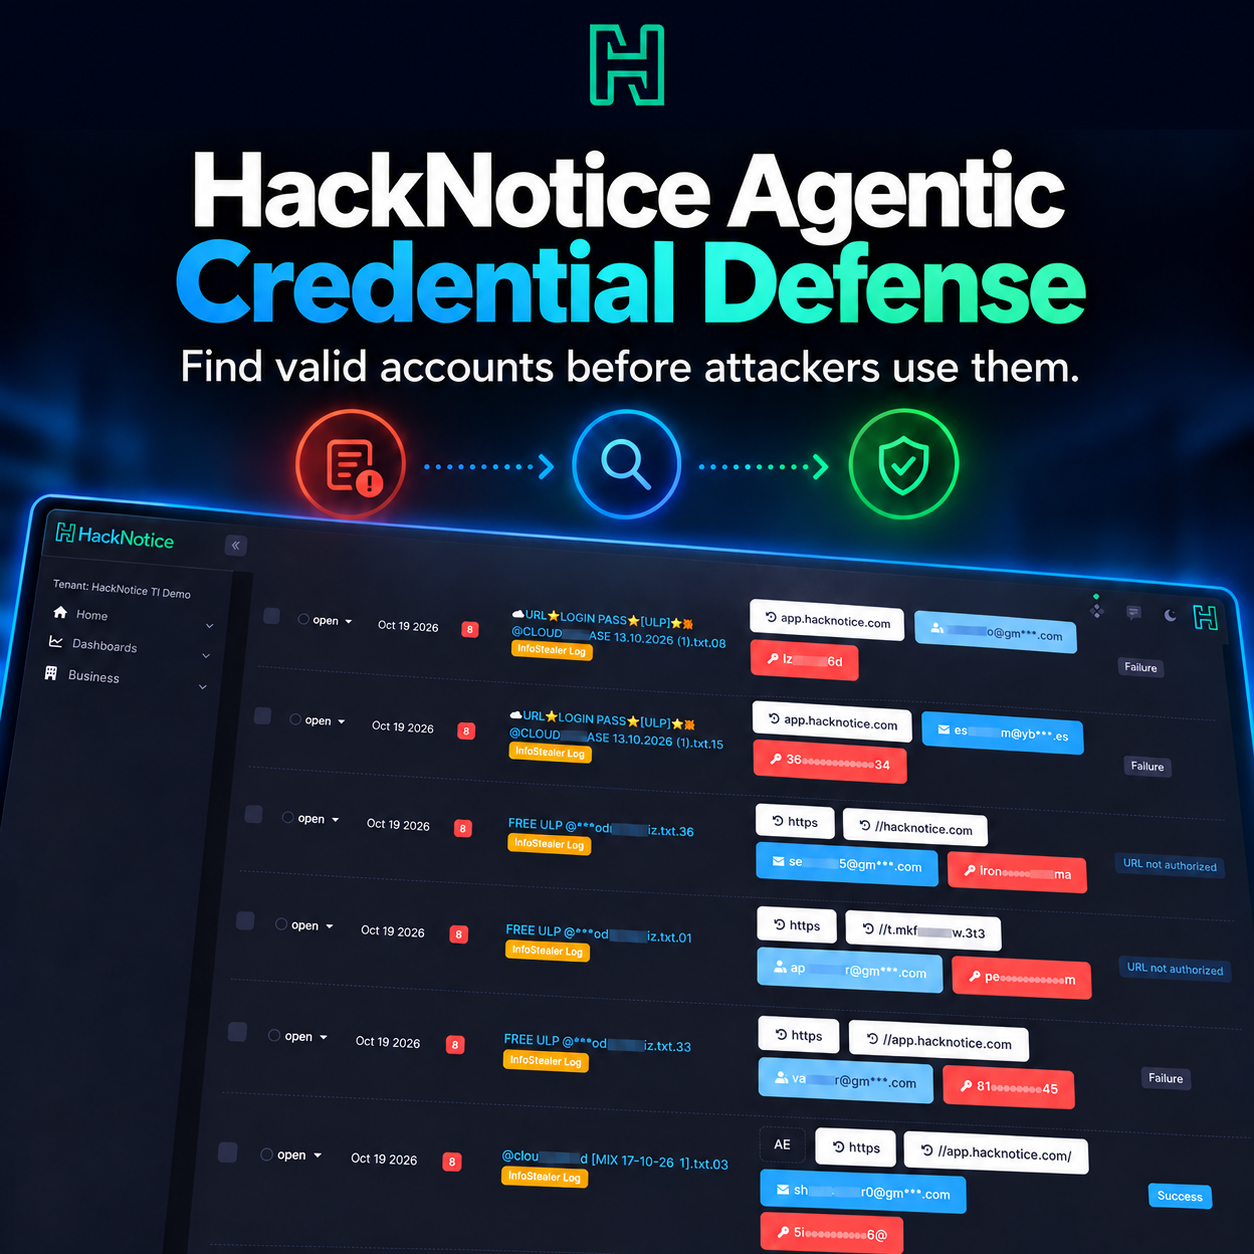
Agentic Credential Defense
AI agent continuously validates stolen credentials, captures proof of valid access, and triggers invalidation to interrupt account takeover.
AUSTIN, TX, UNITED STATES, October 30, 2026 /EINPresswire.com/ -- HackNotice today announced Agentic Credential Defense, a new service powered by an AI agent that works continuously to test credentials from infostealer logs and credential dumps, identify valid accounts, capture proof of successful authentication, and trigger credential invalidation before attackers can reuse the same access.
Security teams receive large volumes of exposed credentials, but exposure alone does not show which accounts remain active. Agentic Credential Defense moves beyond raw credential intelligence. It continuously evaluates newly discovered credentials against customer-authorized login endpoints and authentication flows, then focuses the response on confirmed valid accounts.
"We trained an AI agent to hack our customers faster than hackers can," said Steve Thomas, CEO and Founder of HackNotice. "The difference is authorization, proof, and speed. The agent tests only within the customer's approved scope, proves which accounts are valid, and can immediately trigger invalidation before a criminal uses the same credential."
From stolen credential to closed door
Customers define the domains, applications, login URLs, authentication methods, and testing scope they authorize. HackNotice reviews the configuration before activation. Once enabled, the HackNotice Credential Defense Agent works continuously across infostealer-based credentials and customer-authorized credential dumps, including websites and authentication flows it has not encountered before.
The service provides a four-stage workflow:
1. Collect. HackNotice continuously ingests infostealer logs, credential dumps, and other exposed account data.
2. Test. The agent attempts authentication only against customer-authorized applications and login endpoints.
3. Prove. When authentication succeeds, HackNotice records the valid account and captures evidence of the authenticated session so the customer can act on a confirmed risk.
4. Invalidate. HackNotice can send the customer a credential-invalidation request containing the login URL and email address. The password is never sent. The customer can then reset the password, revoke active sessions, and review the account for unauthorized activity.
The result is an end-to-end response to account takeover risk: discover the credential, determine whether the account is valid, preserve proof, and close the access path.
Why valid accounts matter
Valid Accounts is MITRE ATT&CK technique T1078. MITRE notes that adversaries may abuse existing accounts for Initial Access, Persistence, Privilege Escalation, and Defense Evasion. Because the activity uses legitimate credentials and normal authentication paths, it can be difficult to distinguish from an authorized user.
HackNotice research covering ransomware events during the prior 90 days found that 83% of victims had valid accounts used, abused, or misused by the ransomware group. The accounts supported initial access, persistence, privilege escalation, defense evasion, or a combination of those objectives.
For enterprises, a stolen credential tied to a valid account can expose email, SaaS applications, remote access, cloud services, and internal systems. For consumer-facing businesses, it can lead directly to account takeover, fraud, customer loss, and reputational damage.
Authorized testing and controlled response
Agentic Credential Defense is designed for authorized defensive testing. Customers define and attest to the permitted scope, HackNotice reviews configurations before activation, and testing is limited to approved domains, applications, and login endpoints. The service does not send passwords through the invalidation notification.
Agentic Credential Defense is available today to HackNotice customers and new subscribers. This is the first time HackNotice has offered continuous credential discovery, AI-driven validation, proof capture, and automated invalidation as one complete workflow.
Learn more at https://hacknotice.com/
About HackNotice
HackNotice delivers operational adversary intelligence for third-party and identity security. The platform continuously monitors ransomware leak sites, underground forums, breach datasets, infostealer malware logs, criminal marketplaces, and threat actor activity, automates investigation, and delivers actionable intelligence to security teams in real time. HackNotice is headquartered in Austin, Texas.
Learn more at https://hacknotice.com/
Source: MITRE ATT&CK Valid Accounts, T1078: https://attack.mitre.org/techniques/T1078/
The 83% figure is based on HackNotice research covering ransomware events during the prior 90 days.
Stephen Thomas
Hack Notice, Inc.
Visit us on social media:
LinkedIn
Bluesky
Instagram
Facebook
YouTube
TikTok
X
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
